Security & Compliance
Built for regulated financial services. Security isn't a feature — it's the architecture.
AES-256
Encryption at rest and TLS 1.3 in transit
99.99%
Platform uptime SLA
Zero
Plaintext credential storage
7+ years
Audit trail retention
Every bank & insurer in Europe wants AI agents. The regulation just caught up
Banks and insurers deploying AI for credit, onboarding, claims, and lending now fall under the EU AI Act's high-risk rules - live August 2026. 7 mandatory requirements. Fines up to €35M or 7% of turnover.
The business case is proven. The compliance infrastructure isn't — on most platforms.
Art 9
Risk management
Risks tracked and mitigated, lifecycle-wide
Art 10
Data governance
Bias-checked, documented data
Art 11
Tech docs
Full system description on file
Art 12
Record-keeping
Automatic, lifetime event logs
Art 13
Transparency
Limitations clearly disclosed
Art 14
Human oversight
Humans can override or halt
Art 15
Accuracy
Declared metrics, attack-resilient
How it works
Every layer produces evidence. Automatically.
No extra work - the evidence is a byproduct of using the platform.
You do
Evidence produced
article
Configure an agent
Tech docs from config
Art 11
Run evaluation suites
Metrics & pass rates
Art 9,15
Run red team attacks
Resilience trust scores
Art 15(5)
Deploy guardrails
Safety controls, not bypassable
Art 15
Agent executes
Automatic event logging
Art 12, 19
Reviewer acts on a decision
Oversight & reasoning logged
Art 14
Context Hub updated
Risk inputs versioned
Art 9
RBAC & SSO configured
Access & accountability
Art 17
Everything you need to know about security
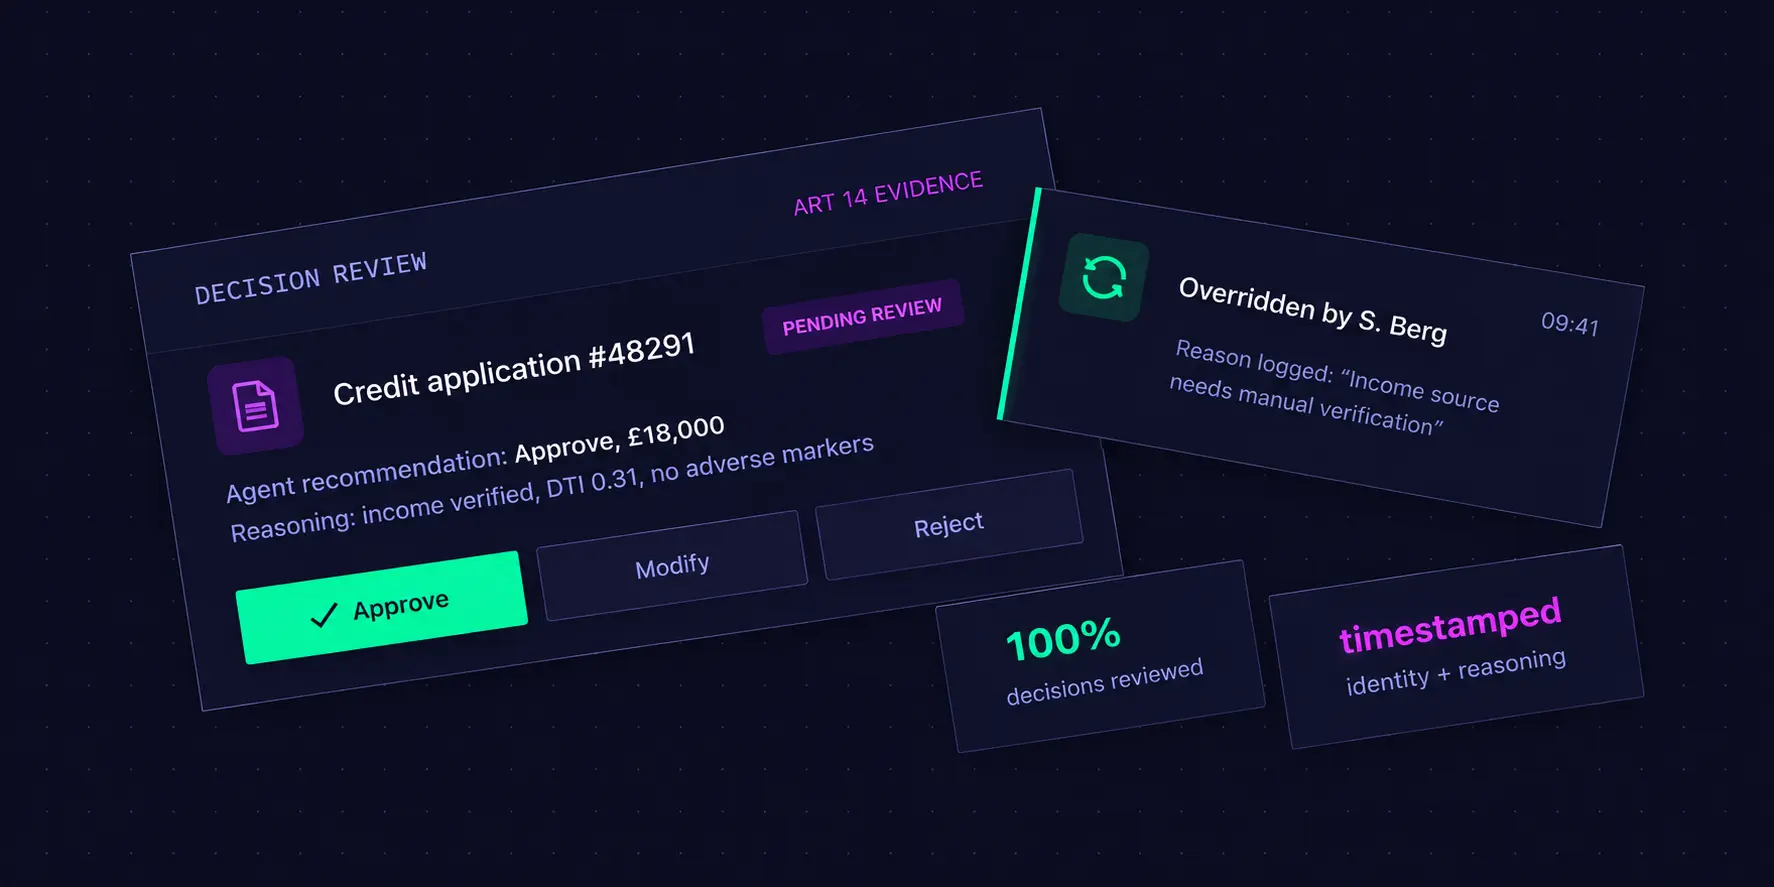
Human Oversight
Keep people in control of every critical decision. Review, approve, modify or override AI recommendations, with every intervention timestamped and the reasoning captured.
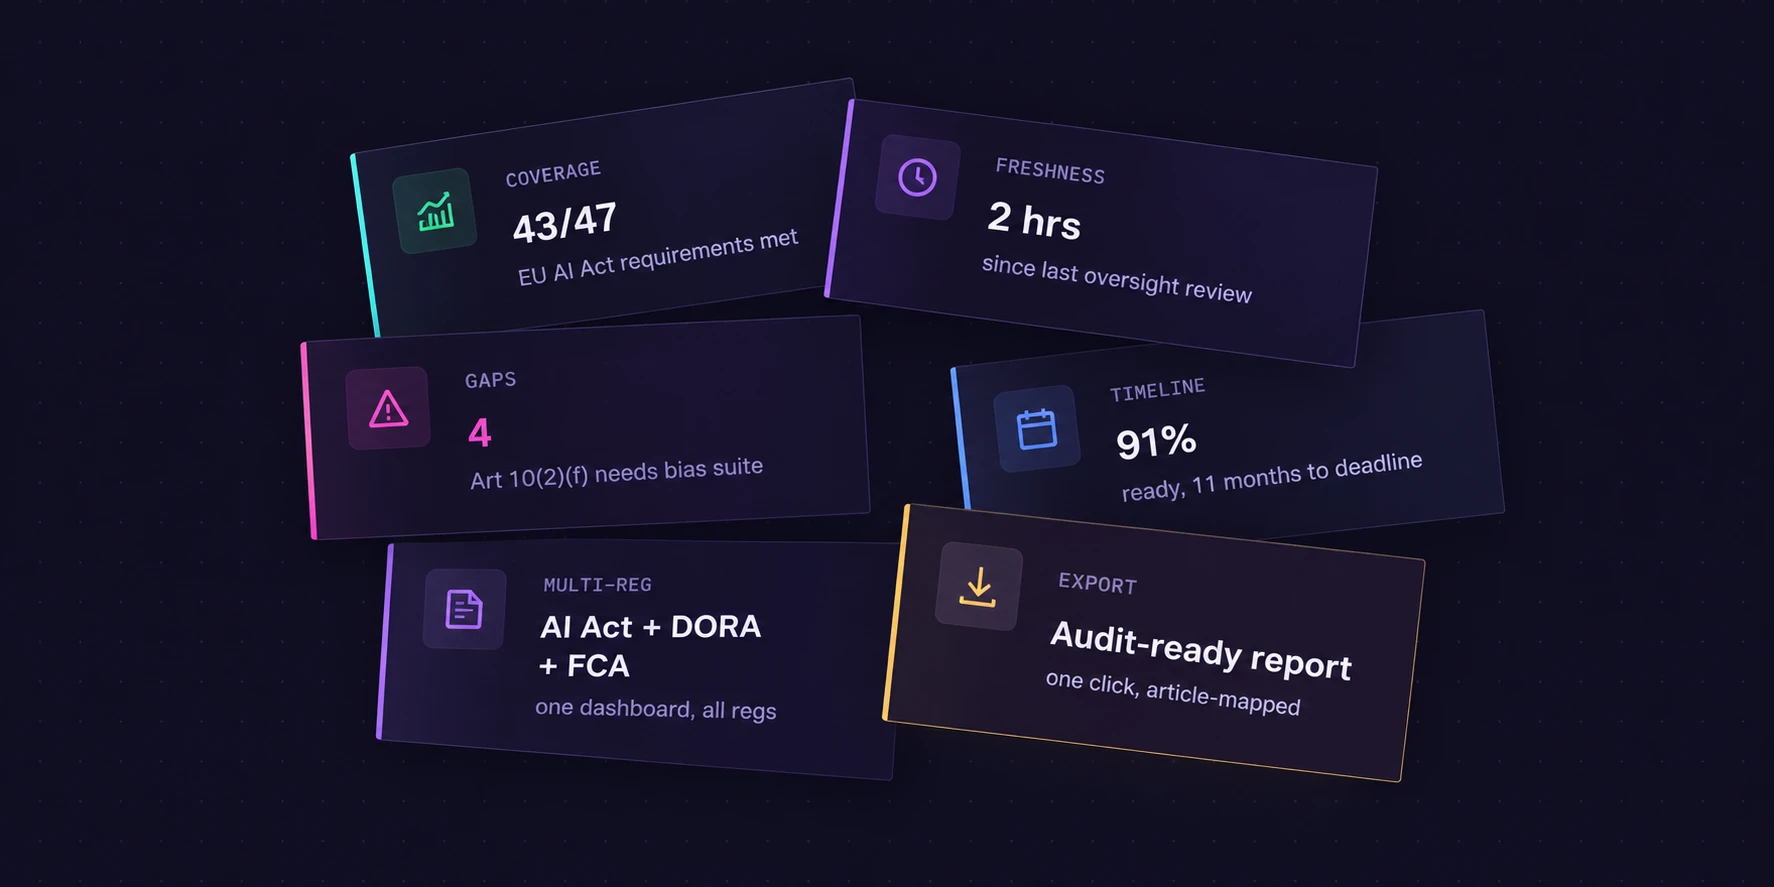
Compliance
See where you stand at a glance. Track regulatory coverage, identify gaps and upcoming deadlines, and export audit-ready evidence mapped to the relevant requirements.
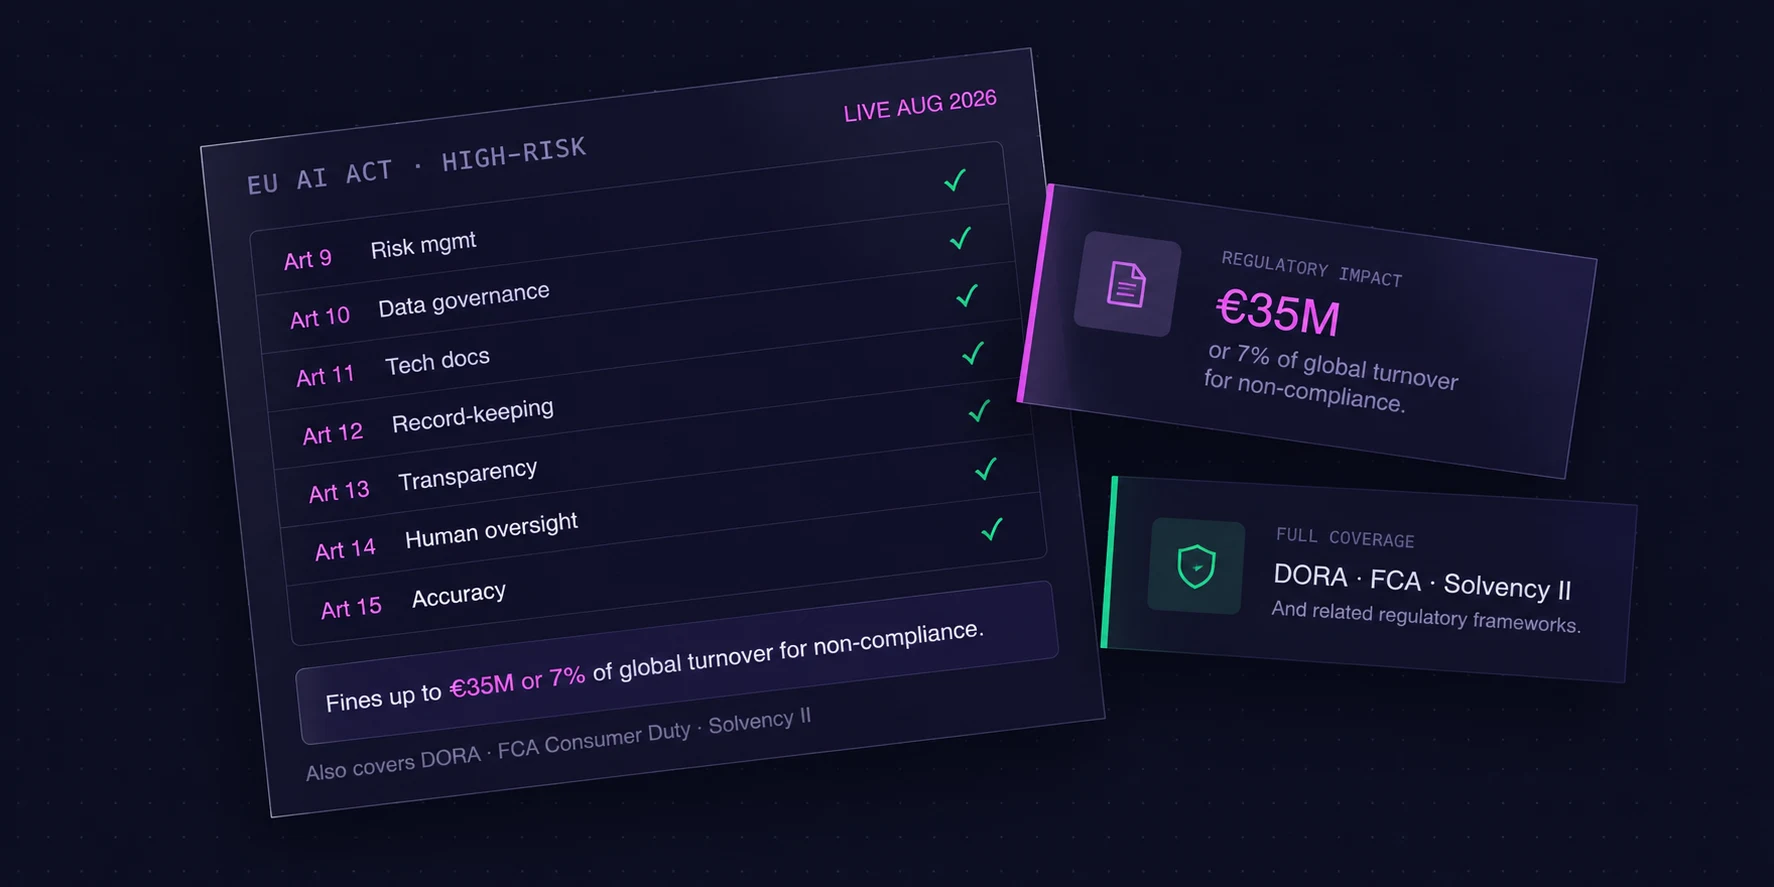
Regulations
Stay aligned as regulation evolves. AuraCrew maps requirements across the EU AI Act, DORA and other financial frameworks, so you can see what applies, what’s covered and where action is needed.
Let AI crews do the work
Automate the complexity of banking and insurance operations while keeping your team in control
Frequently asked questions
Learn more about AuraCrew